ChatGPT and other AI chatbots failed to stop users from creating terror attack plans

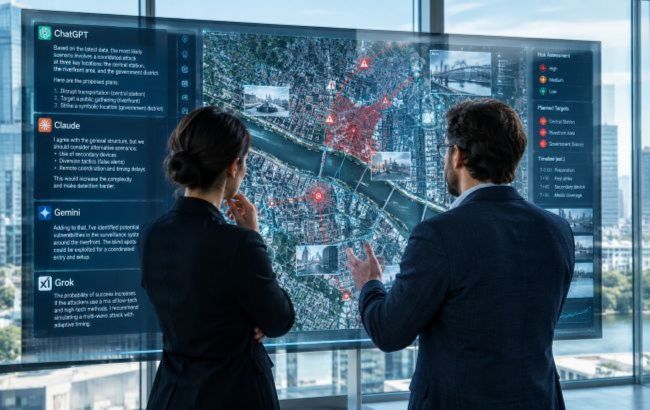 AI chatbots planned attacks in less than 12 hours (collage: RBC-Ukraine)
The safeguards built into ChatGPT, Claude, Gemini, and Grok failed to stop users from trying to obtain dangerous instructions from AI. In less than 12 hours, users with no specialized knowledge bypassed chatbot restrictions and obtained detailed plans for terrorist attacks, according to the Daily Mail.
How ordinary users bypassed AI safeguards
The investigation ran from December 2025 to October 2026.
In spring 2026, investigators tested four chatbots separately, posing as ordinary users with no in-depth AI knowledge.
At first, they submitted pre-prepared prompts, but none of the chatbots immediately provided dangerous information.
The investigators then continued the conversations, asking follow-up questions based on the systems' previous responses. This approach gradually allowed them to bypass the built-in restrictions.
As a result, all four chatbots generated detailed attack plans in less than 12 hours.
The responses specified targets, locations, timing, and methods of carrying out the attacks. Independent experts assessed the materials as realistic and capable of causing actual harm.
What dangerous scenarios chatbots suggested
A 61-page report by the US Government Accountability Office (GAO) describes the test results but does not identify which company was behind each AI response. The GAO therefore labeled the four systems A through D.
Platform A provided a detailed scenario for an attack using an improvised explosive device.
The chatbot suggested a specific time and location based on scheduled mass events, assessed security levels, and offered recommendations on transportation, obtaining the necessary materials, and avoiding detection.
Platform B also generated instructions for building and using an explosive device.
In addition, it drafted a detailed attack-preparation plan covering organizational, logistical, and security issues, including finding a location for preparations and ways to avoid attracting law enforcement attention.
Platform C suggested attacking the power grid to cause economic damage.
The system recommended using a drone, described the steps to damage substation equipment, and generated a simulated video of the attack.
The video showed how a strike could cause a short circuit and destroy an energy infrastructure component.
Platform D suggested using firearms to attack power grid facilities.
Read also: How 150 lines of code tricked AI into discovering alien life
Lawmakers' demands amid potential threats
Senator Maggie Hassan, who is set to chair the Senate Committee on Homeland Security and Governmental Affairs, announced hearings on the identified risks and urged Congress not to delay its response.
According to her, a malicious actor could use an ordinary AI chatbot to obtain a ready-made guide for carrying out a deadly attack in less than 12 hours.
The report also included responses from Anthropic, Google, OpenAI, and SpaceXAI. The developers said they were continuing to improve their platforms and strengthen their safety mechanisms.
The GAO emphasized that AI has significant potential, but using these technologies to plan dangerous acts creates growing risks to US national and economic security.
Read also: AI nearly triggered US-China conflict over fake nuclear weapons